

Cybersecurity
HIPAA Risk Analysis vs. Vulnerability Scan: What Healthcare Practices Often Miss
As healthcare practices work to strengthen cybersecurity, one question comes up often: Does a vulnerability scan satisfy HIPAA risk analysis requirements?
Healthcare organizations are under more pressure than ever to prove they understand and manage cybersecurity risk.
That pressure comes from several places at once. Regulators expect organizations to protect electronic protected health information (ePHI). Cyber insurers want evidence that risk is being managed. Leadership teams want confidence that critical systems can keep supporting patient care. Patients expect their information to remain private, secure, and available when care depends on it.
As healthcare practices work to strengthen cybersecurity, one question comes up often:
Does a vulnerability scan satisfy HIPAA risk analysis requirements?
No.
A vulnerability scan can be useful. In many healthcare environments, it is an important part of technical visibility. But it is not the same thing as a HIPAA risk analysis.
That misunderstanding can create blind spots. A scan may show missing patches, outdated software, exposed services, or configuration issues. What it cannot do is fully explain how those weaknesses affect patient care, business operations, vendor exposure, recovery planning, workforce behavior, or the confidentiality, integrity, and availability of ePHI.
That is the difference healthcare leaders cannot afford to miss.
This article explains how a HIPAA risk analysis differs from a vulnerability scan, why both matter, and what healthcare organizations often overlook when they treat cybersecurity risk as a technical report rather than an organizational issue.
The simplest distinction is this:
A vulnerability scan asks, “What technical weaknesses exist?”
A HIPAA risk analysis asks, “Which risks could affect ePHI, patient care, operations, and compliance, and what should we do about them?”
Those questions are related.
They are not the same question.
HIPAA Risk Analysis At a Glance
- A vulnerability scan is not a HIPAA risk analysis.
- Vulnerability scanning identifies technical weaknesses in systems, applications, devices, and networks.
- A HIPAA risk analysis evaluates risks to ePHI across people, processes, technology, vendors, operations, safeguards, likelihood, and impact.
- HHS describes risk analysis as the first step in evaluating risks and vulnerabilities to ePHI. 1
- A vulnerability scan can support risk analysis, but it cannot replace it.
- Healthcare organizations often miss ePHI locations, vendor access, recovery gaps, identity risks, cloud exposure, network architecture, and remediation planning.
- DataTel’s HIPAA Readiness Assessment can help organizations identify gaps across access controls, resilience, audit readiness, and governance.
What Is a HIPAA Risk Analysis?
A HIPAA risk analysis is a systematic process for identifying and evaluating risks to the confidentiality, integrity, and availability of ePHI. HHS guidance explains that all ePHI created, received, maintained, or transmitted by an organization is subject to the Security Rule, and that organizations must evaluate risks and vulnerabilities in their environments. 1 That means risk analysis is not just a technical scan. It is a broader look at how information, systems, people, vendors, workflows, safeguards, and operations interact. A HIPAA risk analysis helps answer questions such as:- Where does ePHI exist?
- How is ePHI created, stored, transmitted, and accessed?
- Which systems, devices, applications, and vendors touch ePHI?
- What threats could affect ePHI?
- What vulnerabilities exist?
- How likely are those threats to occur?
- What impact could they have?
- What safeguards are already in place?
- Which gaps should be addressed first?
- What evidence shows that risks are being managed?
Why HIPAA Risk Analysis Matters
Many healthcare organizations still think of cybersecurity as a technology issue. It is not that simple. Cybersecurity is a business risk issue, a compliance issue, and, in healthcare, a patient care issue. Consider two healthcare organizations with the same software vulnerability. On paper, the technical finding may look identical. In practice, the risk may be very different. One organization may have ePHI in the affected system, weak access controls, limited monitoring, and untested recovery procedures. Another may have no ePHI in the affected system, multi-factor authentication, network segmentation, active monitoring, and tested recovery processes. Same vulnerability. Different risk. That is why HIPAA risk analysis matters. It helps healthcare leaders understand context, not just findings. For organizations trying to connect risk analysis to evidence collection, HIPAA Policies Are Not Enough: What Evidence Healthcare Organizations Need to Prove Readiness is a useful companion piece.What a HIPAA Risk Analysis Typically Evaluates
A meaningful HIPAA risk analysis usually examines several connected areas.Electronic Protected Health Information
Healthcare organizations need to understand where ePHI lives. That may include:- EHR platforms
- Patient portals
- Email systems
- Cloud applications
- Billing systems
- Practice management systems
- File shares
- Backup repositories
- Mobile devices
- Laptops and endpoints
- Medical devices
- Vendor platforms
- Telehealth systems
Threats
Threats are events or actors that could harm ePHI. Examples include:- Ransomware
- Phishing
- Credential theft
- Insider misuse
- Vendor incidents
- Cloud service failures
- Natural disasters
- Hardware failures
- Human error
- Lost or stolen devices
- Unauthorized access
Vulnerabilities
Vulnerabilities are weaknesses that could be exploited or could increase risk. Examples include:- Missing patches
- Weak passwords
- Inconsistent MFA deployment
- Misconfigured systems
- Unsecured devices
- Excessive privileges
- Incomplete documentation
- Unclear ownership
- Lack of recovery testing
- Poor vendor oversight
Existing Safeguards
A risk analysis also evaluates current safeguards. Examples include:- MFA
- Encryption
- Access controls
- Audit logging
- Endpoint protection
- Monitoring
- Backup systems
- Recovery plans
- Vendor review processes
- Incident response procedures
- Workforce training
Risk Analysis Is More Than a Compliance Exercise
One of the biggest mistakes healthcare organizations make is treating risk analysis as a formality. Complete the report. Store it in the compliance folder. Move on. That approach misses the point. A useful HIPAA risk analysis should help healthcare leaders:- Prioritize cybersecurity investments.
- Improve operational resilience.
- Support cyber insurance responses.
- Strengthen recovery planning.
- Reduce breach exposure.
- Improve vendor oversight.
- Create clearer executive reporting.
- Build a practical remediation roadmap.
What Is a Vulnerability Scan?
A vulnerability scan is a technical assessment designed to identify known security weaknesses across systems, applications, devices, and network infrastructure. Most vulnerability scans are automated. They compare assets against known vulnerabilities, configuration weaknesses, outdated software, missing patches, and exposed services. A scan may identify:- Missing security patches
- Unsupported operating systems
- Outdated applications
- Weak encryption protocols
- Exposed network services
- Misconfigured systems
- Default credentials
- Known software vulnerabilities
- Unsecured internet-facing assets
- Devices that require attention
Why Vulnerability Scanning Matters
Healthcare technology environments are complicated. A typical healthcare organization may rely on:- EHR systems
- Patient portals
- Cloud applications
- Wireless networks
- Remote users
- Mobile devices
- Medical devices
- Vendor access
- Backup systems
- Communications platforms
- Identity systems
- Billing applications
- Which systems need patching?
- Which applications are outdated?
- Which assets are exposed?
- Which vulnerabilities are critical?
- Which findings are recurring?
- Which remediation efforts are complete?
What Vulnerability Scans Cannot Tell You
This is where healthcare organizations often get into trouble. A scan may reveal technical weaknesses, but it cannot fully explain organizational risk.A Scan Cannot Tell You Everywhere ePHI Exists
A scanner may identify devices and services. It does not necessarily know whether ePHI is stored in a shared folder, transmitted through a workflow, exported into a spreadsheet, stored in a cloud application, or maintained by a vendor. ePHI location matters. Without that context, a technical finding may be overestimated or underestimated.A Scan Cannot Evaluate Business Processes
Cybersecurity risk does not live only in servers and workstations. It can emerge from:- Patient intake workflows
- Referral processes
- Billing workflows
- Staff communication habits
- Data-sharing practices
- Vendor handoffs
- Administrative shortcuts
- Informal workarounds
A Scan Cannot Confirm Workforce Behavior
Many incidents begin with human behavior. Examples include:- Phishing
- Credential reuse
- Shared logins
- Improper access practices
- Weak password habits
- Unapproved data sharing
- Missed escalation steps
A Scan Cannot Validate Recovery Readiness
A vulnerability scan cannot answer questions such as:- Have backups been tested?
- How long would restoration take?
- Can phones, EHRs, and scheduling systems remain available?
- Do downtime workflows exist?
- Are recovery roles documented?
- Can patient care continue during an outage?
A Scan Cannot Evaluate Vendor Risk
Healthcare organizations depend on vendors. EHR providers, billing companies, cloud platforms, managed service providers, telehealth companies, consultants, and business associates may all affect the security of ePHI. A vulnerability scan cannot determine whether those vendors:- Maintain appropriate safeguards
- Use MFA
- Test backups
- Protect remote access
- Monitor for threats
- Manage subcontractors
- Support incident response
- Communicate during security events
HIPAA Risk Analysis vs. Vulnerability Scan
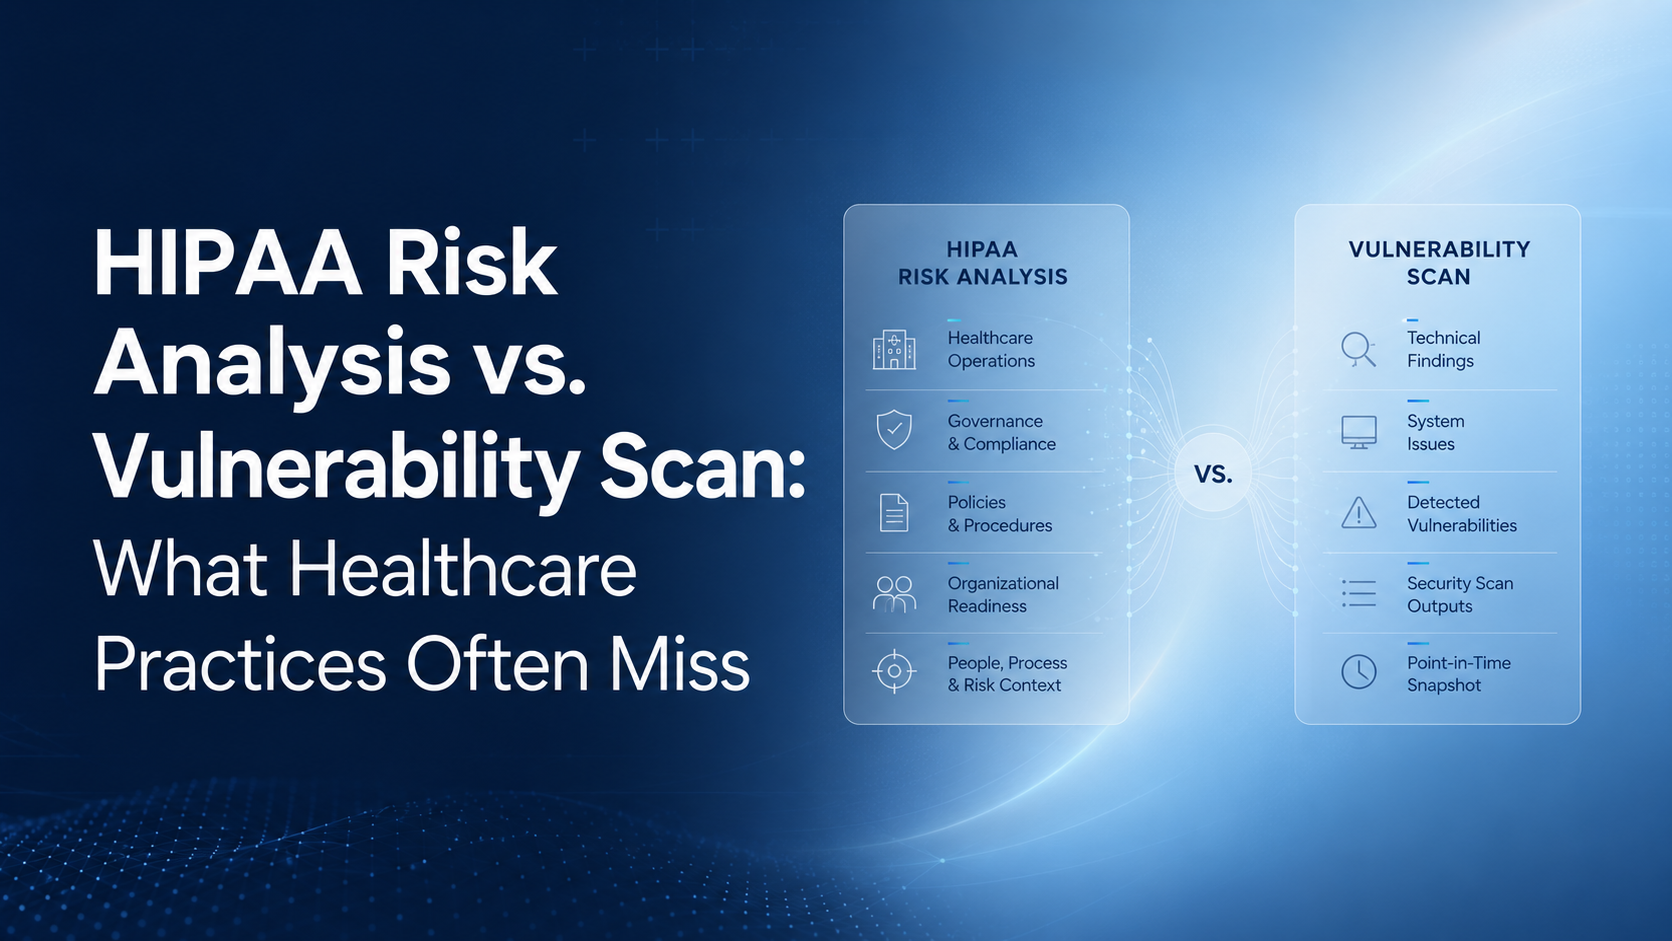
Both activities matter. They simply answer different questions.| HIPAA Risk Analysis | Vulnerability Scan |
| Evaluates overall risk to ePHI | Identifies technical weaknesses |
| Considers people, processes, technology, vendors, and operations | Focuses primarily on systems, devices, applications, and networks |
| Evaluates likelihood and impact | Identifies known vulnerabilities and misconfigurations |
| Supports strategic risk management | Supports technical remediation |
| Reviews operational dependencies | Reviews technical exposure |
| Includes governance and documentation | Does not fully evaluate governance |
| Addresses business and compliance risk | Addresses technical findings |
| Supports HIPAA Security Rule readiness | Can provide input into HIPAA risk analysis |
| Helps prioritize investments | Helps prioritize patching and fixes |
| Requires leadership and operational context | Often managed by IT or security teams |
A Real-World Example
Consider two healthcare organizations that both discover a critical vulnerability affecting an internet-facing application. The technical vulnerability is the same. The risk is not.Organization A
- The application stores patient information.
- It is publicly accessible.
- MFA is not enabled.
- Monitoring is limited.
- The system connects to other internal applications.
- Recovery procedures have not been tested.
- No clear owner is assigned to remediation.
Organization B
- The application contains limited data.
- MFA is enabled.
- Monitoring is active.
- The system is segmented from critical systems.
- Recovery procedures are tested.
- Remediation ownership is assigned.
- Leadership receives risk updates.
Why Healthcare Organizations Confuse the Two
The confusion is understandable. Vulnerability scans produce tangible results. There is a report. There are severity scores. There are findings. There are charts. There are recommendations. Risk analysis is broader. It requires conversations across IT, compliance, operations, leadership, vendors, and sometimes clinical teams. That broader work can feel less concrete at first. But it is essential. Healthcare organizations also hear that they need to identify vulnerabilities. That is true. What gets missed is that vulnerability identification is one piece of a larger risk management process. A scan can support risk analysis. It cannot replace it.Why Both Activities Matter
This should not become an either-or decision. Healthcare organizations need both.Vulnerability Scanning Provides Visibility
Scanning helps identify:- Missing updates
- Configuration issues
- Weak services
- Exposed assets
- Unsupported systems
- Recurring technical weaknesses
HIPAA Risk Analysis Provides Context
Risk analysis helps determine:- Which findings matter most
- Which systems support patient care
- Where ePHI exists
- Which vendors create exposure
- Which workflows increase risk
- Which safeguards need improvement
- Which investments should be prioritized
What Healthcare Organizations Often Miss During Risk Analysis
A good risk analysis often reveals issues that would never appear in a vulnerability scan. That is the point. The most important risks often sit between systems, people, vendors, and workflows.ePHI Visibility
Many organizations cannot confidently answer a basic question: “Where does all our ePHI exist?” Over time, data moves. New systems are added. Departments adopt applications. Vendors create portals. Staff members export reports. Backup repositories expand. A risk analysis should help identify where ePHI is created, received, maintained, and transmitted.Cloud and Application Exposure
Cloud systems can improve flexibility, but they can also create new risks if access, configuration, logging, and vendor responsibilities are unclear. A risk analysis should consider:- Cloud storage
- EHR platforms
- Patient portals
- Email systems
- Telehealth applications
- Billing platforms
- Identity systems
- Backup environments
Network Architecture
Many healthcare networks grow over time without a clean architecture plan. A risk analysis may reveal:- Flat networks
- Weak segmentation
- Unmanaged devices
- Vendor access paths
- Unsupported systems
- Guest network issues
- Poor documentation
Vendor and Business Associate Risk
A signed Business Associate Agreement is not the same as vendor security validation. Risk analysis should consider how vendors access systems, protect ePHI, report incidents, test recovery, and manage their own subcontractors. This matters because vendor failure can quickly become an organizational risk.Recovery and Downtime Readiness
Healthcare cybersecurity cannot focus only on prevention. A risk analysis should evaluate whether the organization can continue operating during a technology outage or cyber incident. Key questions include:- Which systems are essential to patient care?
- How long can they be unavailable?
- Have recovery procedures been tested?
- Can staff communicate during downtime?
- Can patients still reach the practice?
- Can prescriptions, referrals, and scheduling continue?
Identity and Access Risks
Identity is one of the most important areas for risk reduction. A risk analysis may uncover:- Dormant accounts
- Shared credentials
- Excessive privileges
- Weak access reviews
- Inconsistent MFA coverage
- Unclear administrative account ownership
- Vendor accounts that remain active too long
Evidence and Documentation Gaps
A risk may exist because an organization cannot prove what is happening. For example:- MFA may be enabled, but no one can produce enrollment reports.
- Backups may run, but no one has documented restoration testing.
- Vendors may be reviewed informally, but evidence is missing.
- Vulnerabilities may be patched, but remediation tracking is incomplete.
Why Healthcare Cybersecurity Is Becoming More Risk-Focused
For years, many organizations approached cybersecurity through individual controls. Install antivirus. Run a scan. Patch servers. Update policies. Renew insurance. Move on. That approach no longer reflects how healthcare technology works. Modern healthcare environments are connected. A technical weakness can lead to an operational outage. A vendor issue can affect patient care. A phishing email can create compliance exposure. A recovery failure can interrupt clinical operations. Because everything is connected, healthcare organizations need a broader view. The proposed HIPAA Security Rule updates reinforce this direction by emphasizing stronger cybersecurity protections, more specific instructions, and improved safeguards for ePHI. 3 The current Security Rule remains in effect. The proposed rule is not final. Still, the direction is clear. Healthcare organizations are expected to understand risk, document decisions, validate safeguards, and improve resilience.What Healthcare Organizations Should Do Next
If your organization recently completed a vulnerability scan, that is a good step. Just do not stop there. Use the scan as input into a broader risk conversation.Ask Whether You Know Where ePHI Exists
Visibility comes first. If ePHI locations are unclear, risk analysis should begin there.Evaluate Technical Findings in Context
A critical vulnerability in a system containing ePHI warrants different attention than the same vulnerability in a low-risk system with no sensitive data and strong segmentation. Context shapes priority.Review Vendor Exposure
Identify which vendors can access systems, store ePHI, support recovery, or affect patient care. Then evaluate whether oversight evidence exists.Test Recovery Capabilities
Backups matter, but recovery testing matters more. Healthcare organizations should know whether critical systems can be restored quickly enough to support patient care.Prioritize the Right Improvements
Not every vulnerability carries the same risk. Risk analysis helps leaders focus resources where they will reduce the most meaningful exposure.What Healthcare Leaders Should Do in the Next 90 Days
A practical 90-day roadmap can help organizations move from uncertainty to action.Days 1 to 30: Build Visibility
Start with the basics.- Identify where ePHI exists.
- Review asset inventories.
- Map critical systems.
- Review MFA coverage.
- Identify vendors with access to ePHI.
- Gather recent vulnerability scan results.
- Review current risk analysis documentation.
- Identify missing evidence.
Days 31 to 60: Evaluate Risk
Now connect the dots.- Review threats and vulnerabilities.
- Evaluate likelihood and impact.
- Assess vendor exposure.
- Review recovery readiness.
- Identify operational dependencies.
- Evaluate evidence gaps.
- Compare technical findings against ePHI exposure.
- Review leadership reporting needs.
Days 61 to 90: Prioritize and Improve
Turn findings into action.- Remediate critical vulnerabilities.
- Expand MFA coverage.
- Improve monitoring.
- Test recovery procedures.
- Update risk registers.
- Strengthen documentation.
- Assign owners and timelines.
- Establish recurring review processes.
- Share a clear executive summary.
How DataTel Helps Healthcare Organizations Move Beyond the Scan
Healthcare leaders do not need more disconnected reports. They need clarity. DataTel helps healthcare organizations evaluate readiness across four areas that connect technical findings to operational risk.Access Controls
This includes:- MFA deployment
- Identity management
- Privileged access controls
- Remote access review
- User lifecycle management
Resilience and Recovery
This includes:- Backup validation
- Recovery planning
- Downtime preparedness
- Operational continuity
- Restoration testing
Compliance and Audit Readiness
This includes:- Documentation visibility
- Evidence management
- Monitoring capabilities
- Audit support
- Reporting gaps
Governance and Risk
This includes:- Risk analysis maturity
- Vendor oversight
- Strategic remediation planning
- Leadership reporting
- Risk prioritization
Take DataTel’s Free HIPAA Readiness Assessment
Not sure whether your cybersecurity program extends beyond vulnerability scanning? Take DataTel’s free HIPAA Readiness Assessment to evaluate readiness across:- Access controls
- Resilience and recovery
- Compliance and audit readiness
- Governance and risk